Trade secrets, personally identifiable information and regulated data should never go into a public AI tool. In AITF's classification they sit in the Restricted tier, where no AI tools are permitted. Confidential material such as client contracts, financial forecasts and HR records sits in the Confidential tier, and the tool permission matrix maps approved AI tools to that tier.
AI Transformation Framework (AITF) builds this into every client's governance through a data classification of three to five buckets, each tied to its own rules. Classification is the first of AITF's Four Pillars of AI Governance.
How much company data is already going into public AI tools?
PagerDuty's 2026 shadow AI workplace survey, published in June 2026 and drawn from 1,250 office professionals at companies with annual revenue of $500 million or more in the United States, United Kingdom, Australia and Japan, found that 88 percent have shared work-related information with public AI tools. In the same survey, 34 percent shared customer data and 31 percent shared financial information or confidential company documents and strategies.
IBM's 2026 Cost of a Data Breach Report, conducted by the Ponemon Institute and published in July 2026, found that security incidents involving shadow AI, where workers use unapproved AI, more than doubled to 43 percent from 20 percent a year earlier. Those incidents carried an average breach cost of $5.39 million, compared with $4.63 million the year before.
What are the categories of data in an AI data classification?
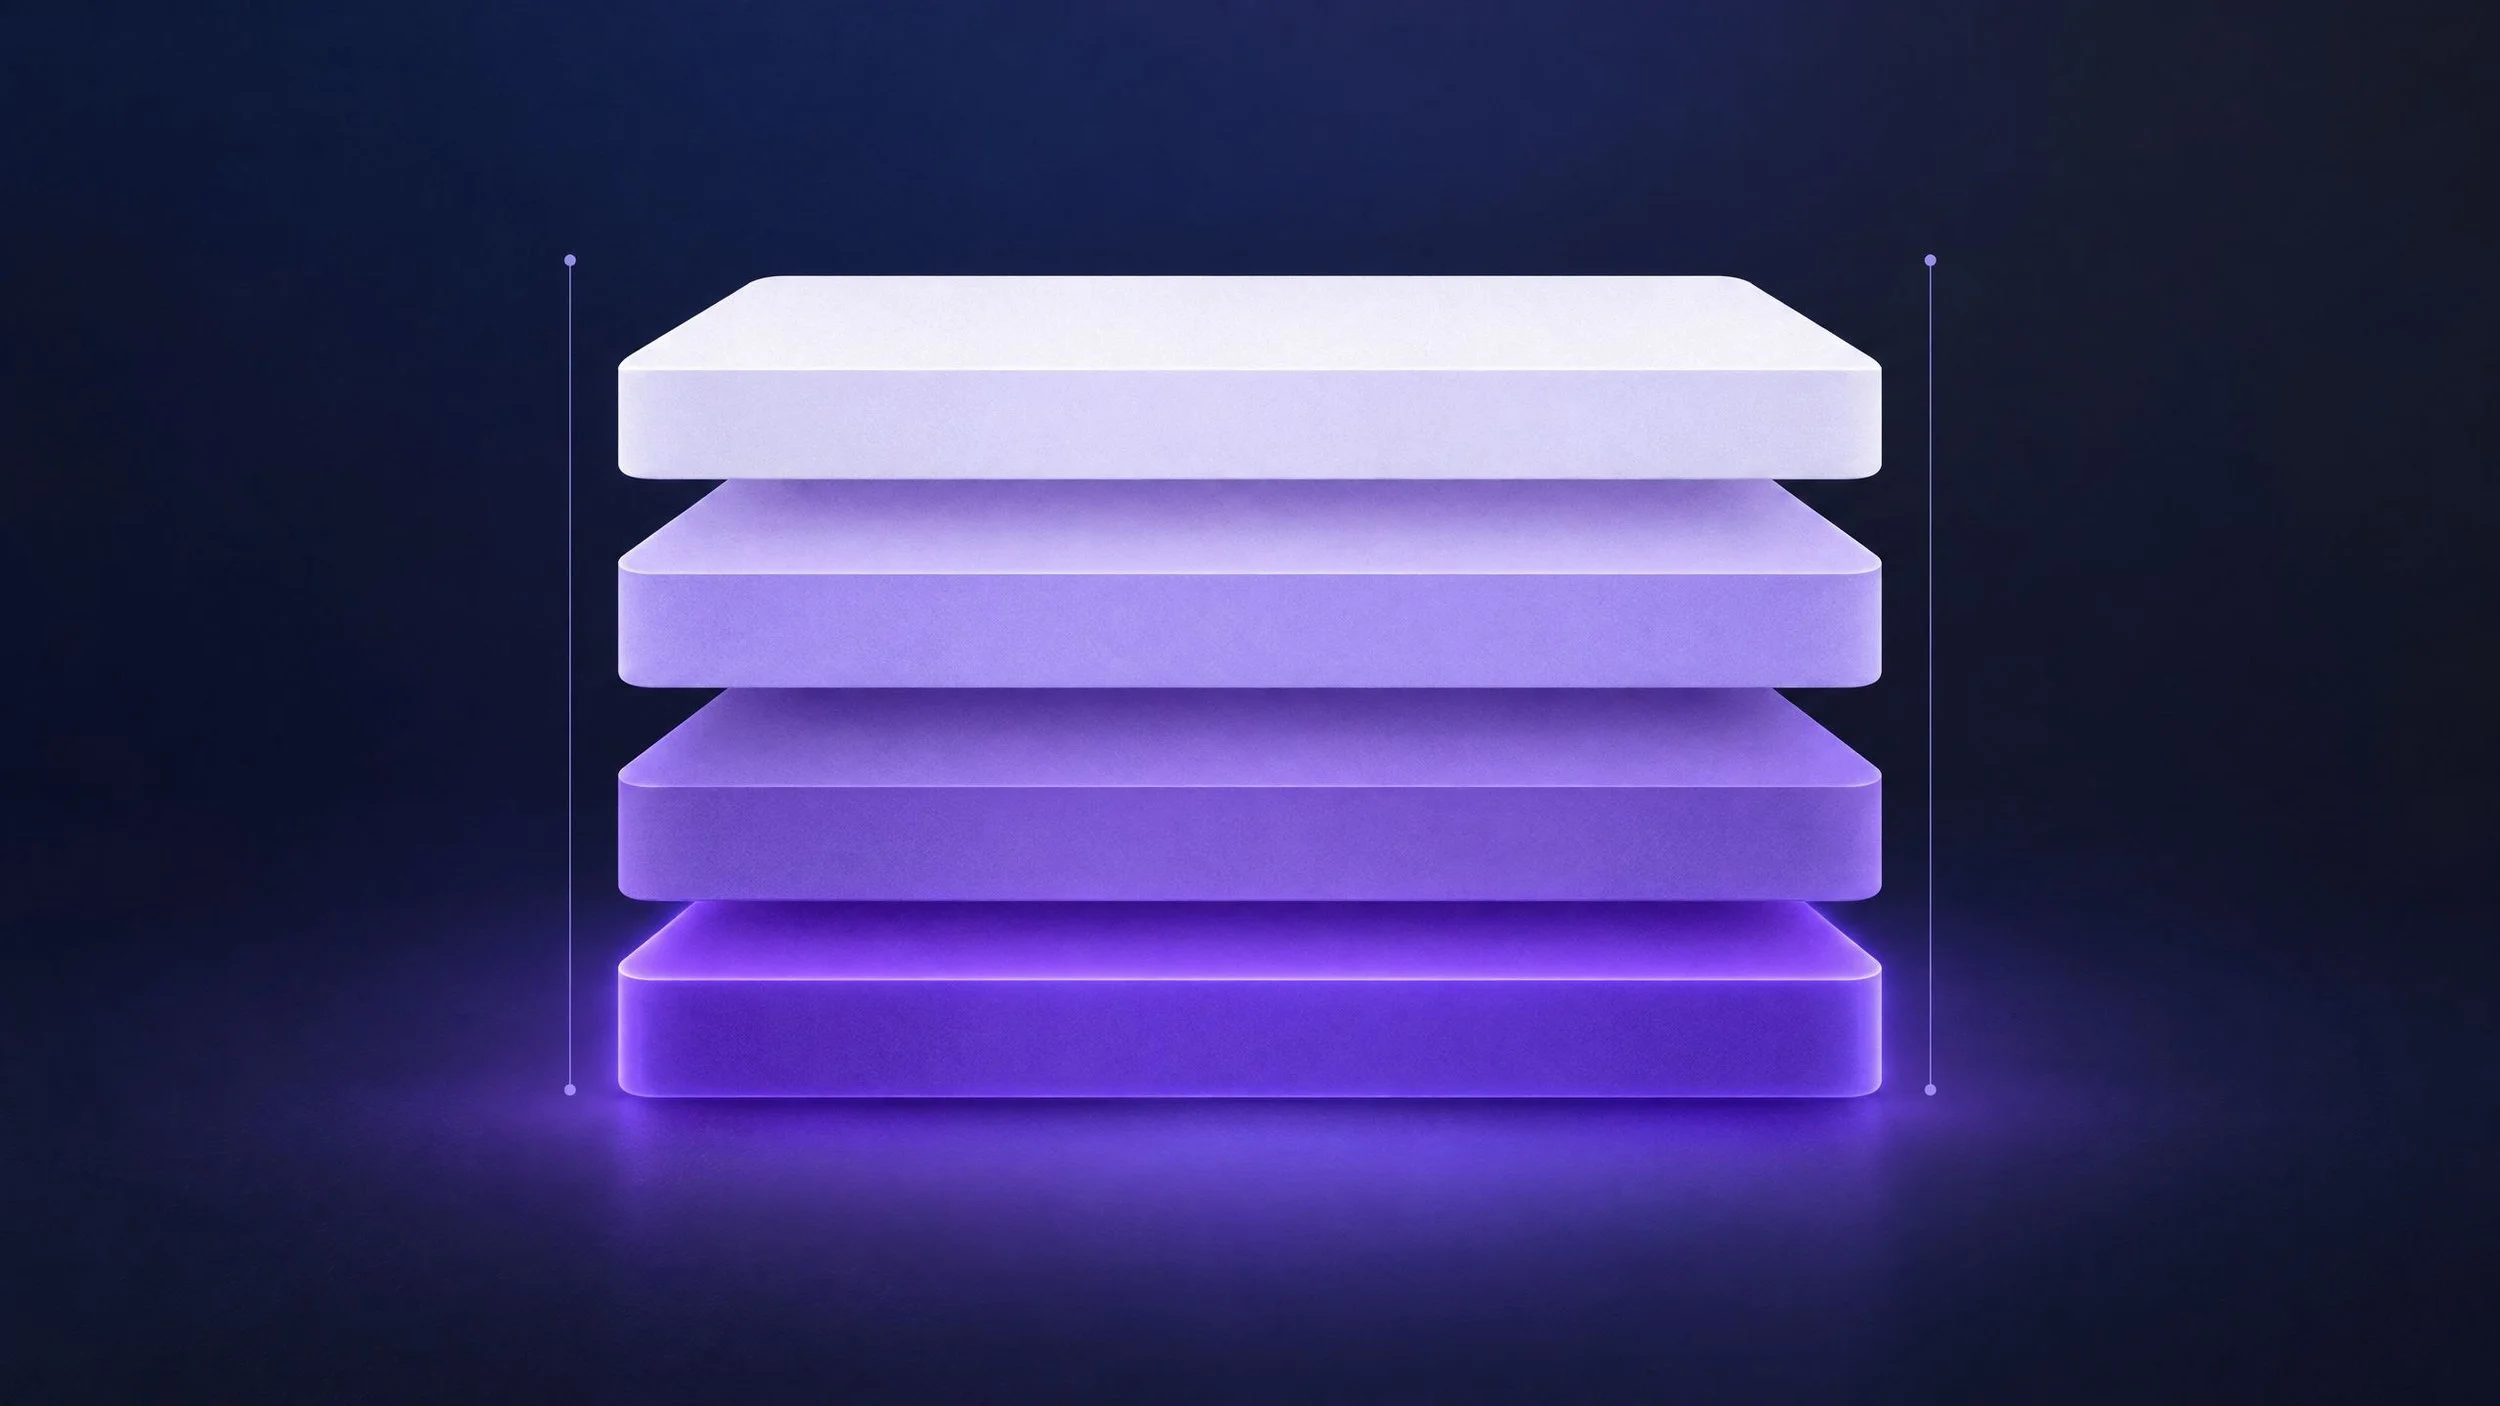
AITF's first pillar defines three to five data buckets so the rules are precise. The four pillars are Classify Your Data, Realistic Policies, Amnesty and Transparency, and Streamlined Access. AITF's example classification uses four tiers:
Public. Marketing copy, published reports and job postings.
Internal. Internal memos, process documentation and meeting notes.
Confidential. Client contracts, financial forecasts and HR records.
Restricted. Trade secrets, personally identifiable information and regulated data, with no AI tools permitted.
Each company drafts its own buckets with three example data types each.
How do we classify the rest of our company data?
AITF's governance workshop sets a three-week timeline:
Week one. Owners confirmed and tasks assigned.
Week two. Data classification buckets drafted.
Week three. Tool permission matrix drafted.
The second pillar, Realistic Policies, ties each bucket to specific rules. The tool permission matrix maps approved AI tools to each bucket. Internal disclosure defines when employees flag AI use in internal deliverables, and external disclosure sets the standard for client-facing and outbound communications.
What makes an AI data policy employees follow?
A tiered policy. AITF's governance workshop states that a blanket AI policy applied to everything paralyzes the company, a single "no AI" rule creates resentment and workarounds, and a tiered policy creates clarity and trust, because each tier carries restrictions proportionate to actual risk.
PagerDuty's survey also found that two-thirds of office professionals used AI tools at work even though they believed company policy prohibited it. ISACA's 2026 AI Pulse Poll, published in May 2026 and drawn from more than 3,400 digital trust professionals, found that 38 percent of organizations have a formal, comprehensive AI policy, 30 percent have a limited policy and 25 percent have no active policy.
How does AITF bring existing AI tool use into the open?
Through the third pillar, Amnesty and Transparency, in three steps. Leadership sends an Amnesty Memo declaring a no-penalty window for disclosing current AI tool use. A simple, anonymous survey maps which tools are in use and where. Employees then train on the new policy.
For more, read What Is Shadow AI and Why Is It a Governance Risk?
How does AITF vet an AI tool before approving it?
The fourth pillar, Streamlined Access and Experimentation, gives employees a fast path to request tools. Each request runs through a 5-point vetting checklist covering data handling, vendor security, compliance, access scope and rollback plan, and the program sets a reasonable SLA for approving or denying requests. The Governance-in-a-Box checklist adds a vendor and contract review covering data retention, training on customer data and security controls.
For vendor questions, read What to Ask an AI Vendor Before You Sign.
Who should own AI governance in a company?
One accountable leader. The first item in AITF's governance rollout checklist is naming an AI owner, and the governance workshop confirms owners and assigns tasks in week one.
For more, read Who Should Own AI Strategy and Governance?
What else do leaders ask about AI data classification?
-
Trade secrets, personally identifiable information and regulated data, which sit in the Restricted tier where no AI tools are permitted.
-
Three to five. AITF's example uses Public, Internal, Confidential and Restricted.
-
With a tool permission matrix that maps each approved AI tool to the data categories it may handle.
Answers to common questions about the program are on the AITF FAQ page. If your team needs data rules it can follow this quarter, I can walk you through what this might look like in your own business in just 20 minutes. Book a time on my calendar.
Delcie Bean is the founder of AI Transformation Framework and CEO of Buildkin and Paragus IT. He built Paragus IT from a company he founded at fourteen into a 100 percent employee-owned IT firm headquartered in Hadley, Massachusetts. With AITF clients, he sets the standard for what a governed AI program looks like and holds leadership teams accountable for their decisions. Meet Delcie and the AITF coaches.